ToothPic Caller Verification
A deepfake has no camera sensor. Prove the caller in one tap.
Generative AI now clones a person’s voice and face in real time. ToothPic moves trust to the physical camera sensor of the caller’s smartphone: a deepfake has no sensor, so it cannot answer the challenge.
wired out of an Italian bank in 2026 after an AI voice-clone and fake-executive scam. Detection scores pixels and guesses. Possession asks the device to sign — and a deepfake has no device.
The deepfake isn’t detected. It’s disqualified.
How it works
Out-of-band. Hardware-signed. Instant.
Directory
Public keys are already in your backend.
Challenge
One tap sends a push to the claimed caller.
Sign
The real sensor regenerates its key and signs the challenge.
Verify
The verifier’s device checks the signature against the stored public key.
Verdict
✓ genuine
✕ deepfake or wrong device.
Live call verification
Six steps. One tap. No secrets stored.
Robert (the verifier, on Android) wants to be sure that Camila (on iPhone) is really on the call. Here is what each of them sees.
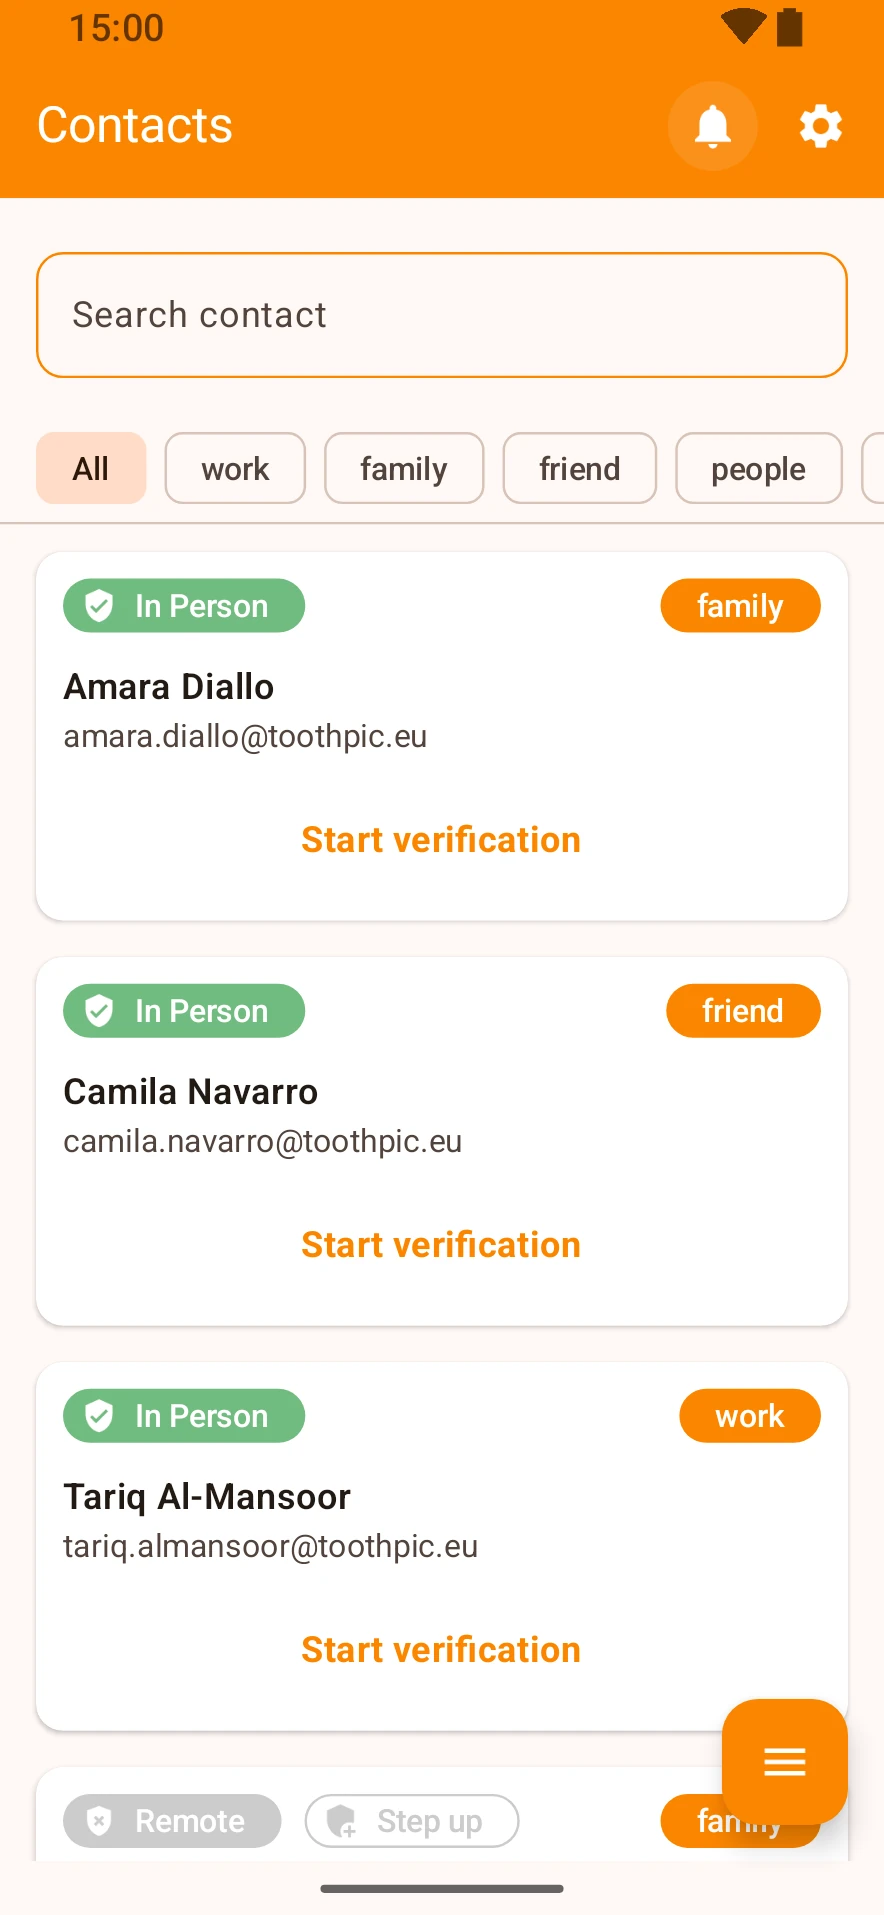
Search directory
Robert opens Caller Verification during the call and finds Camila.
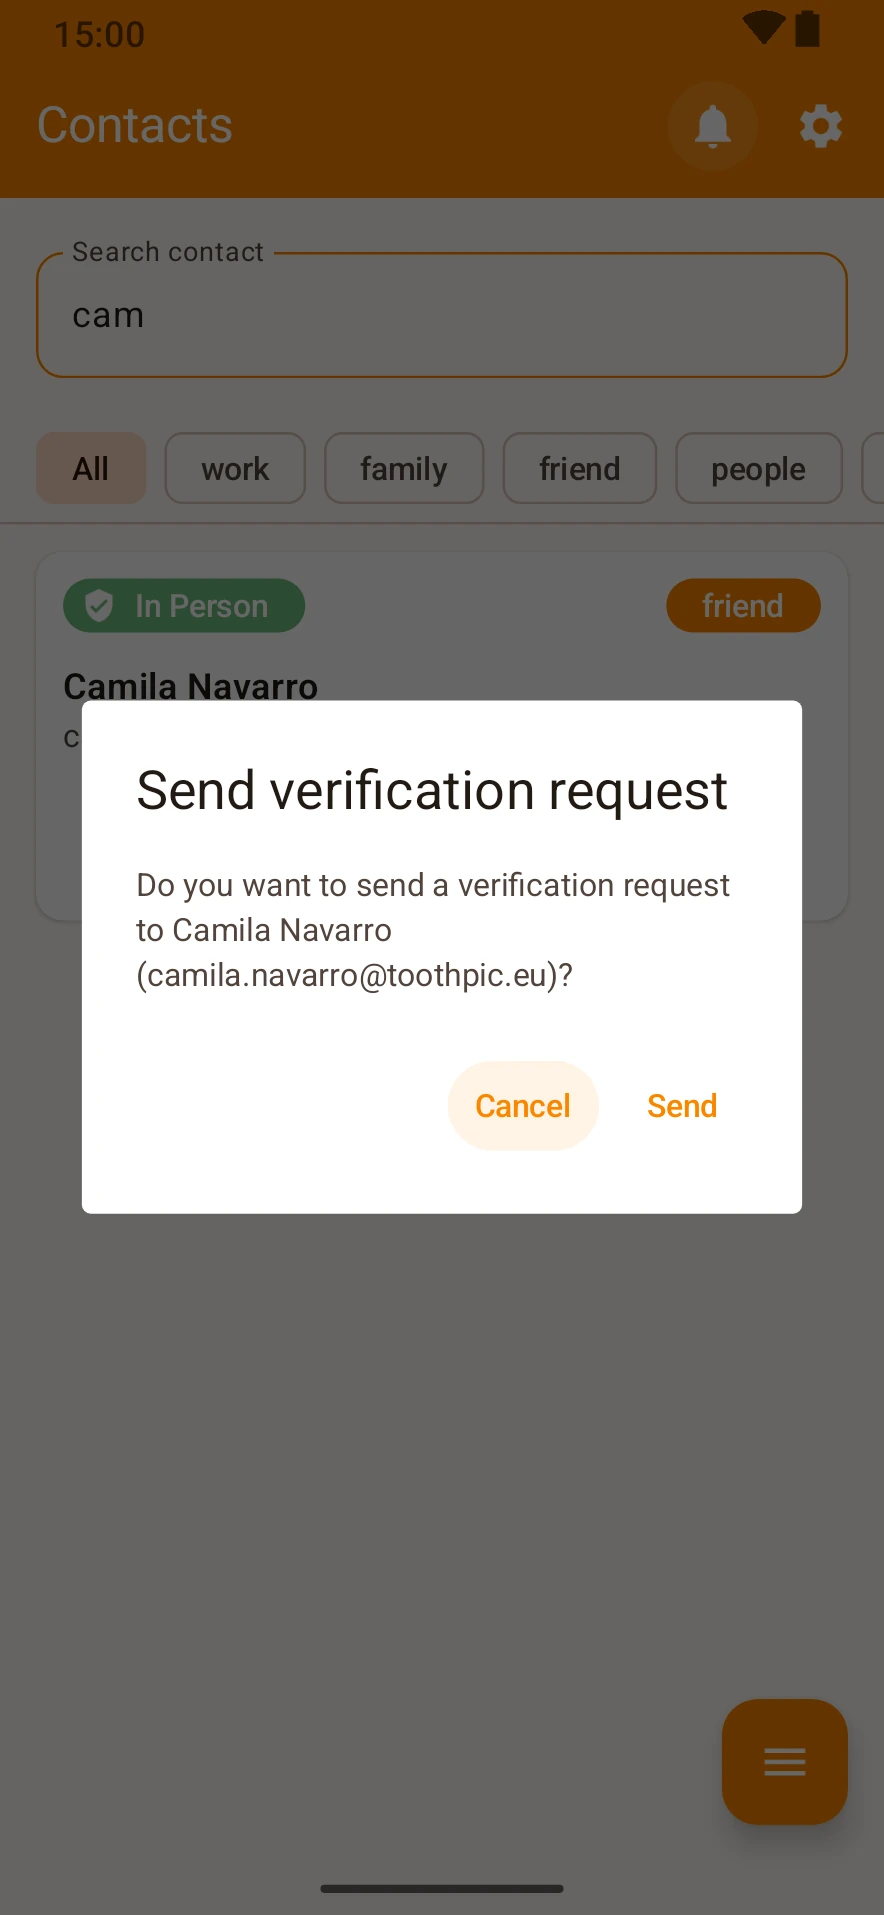
Send challenge
A one-time challenge is created locally and sent out-of-band.
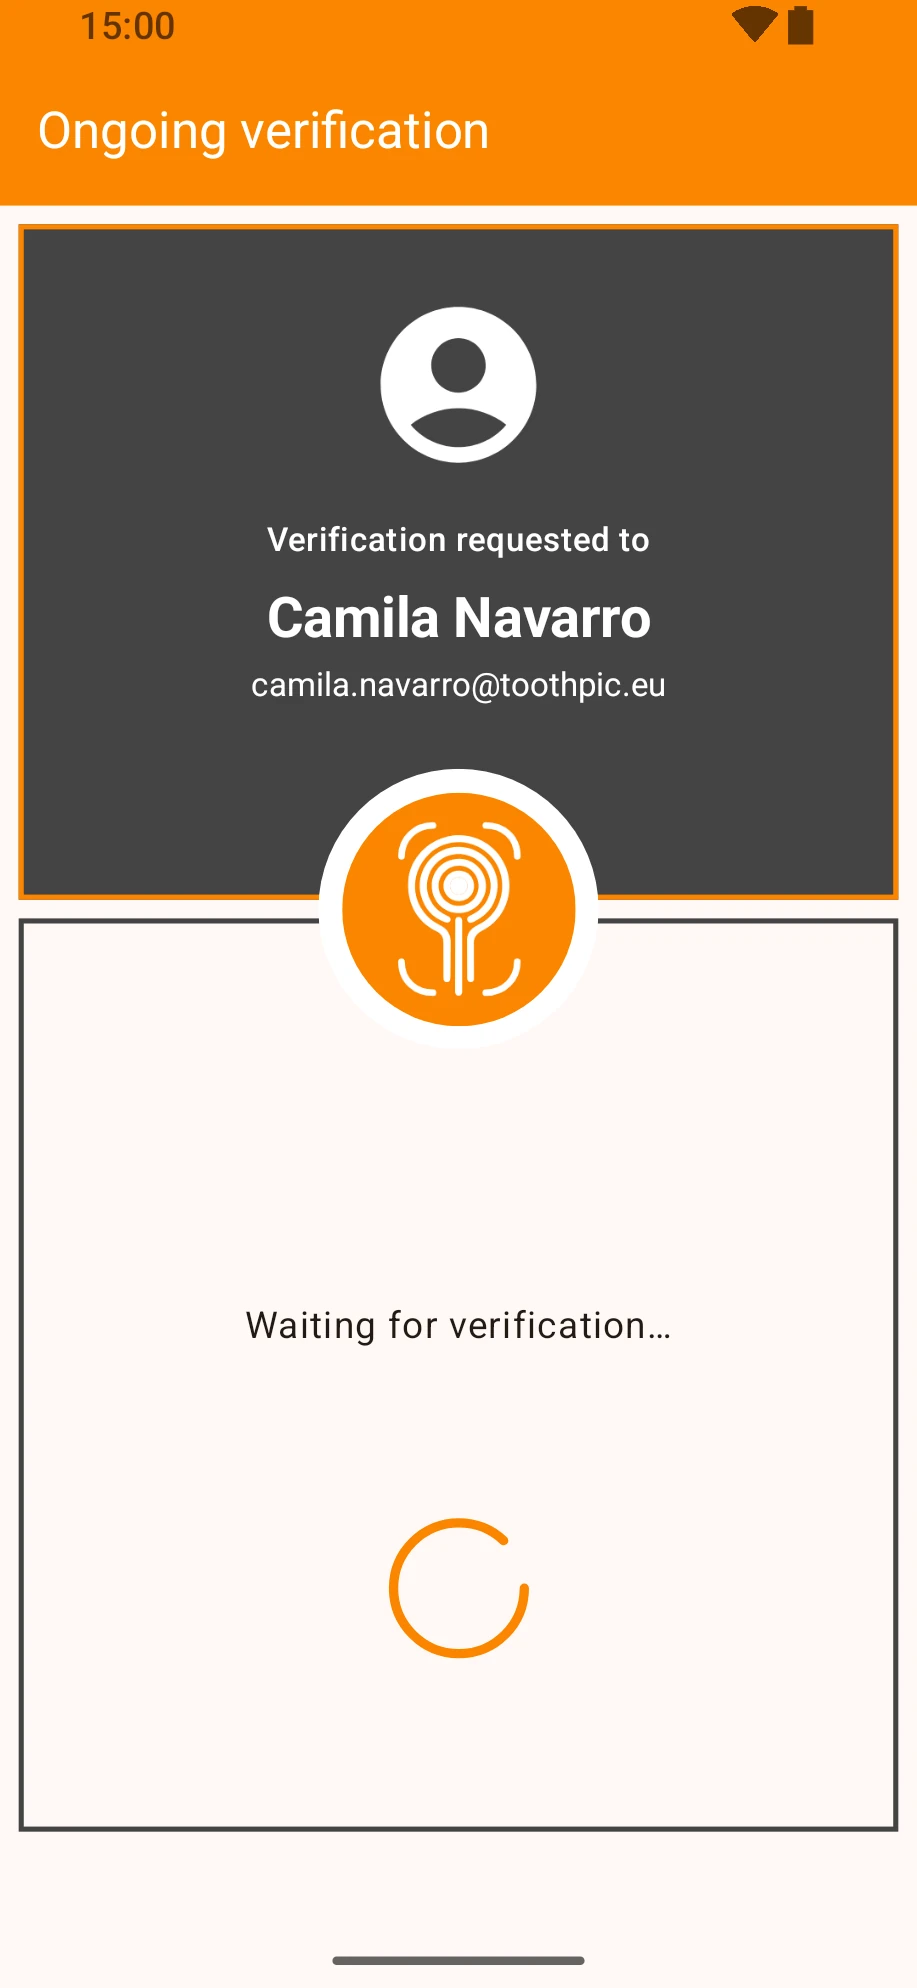
Waiting
The push is delivered; Robert waits for the signature.
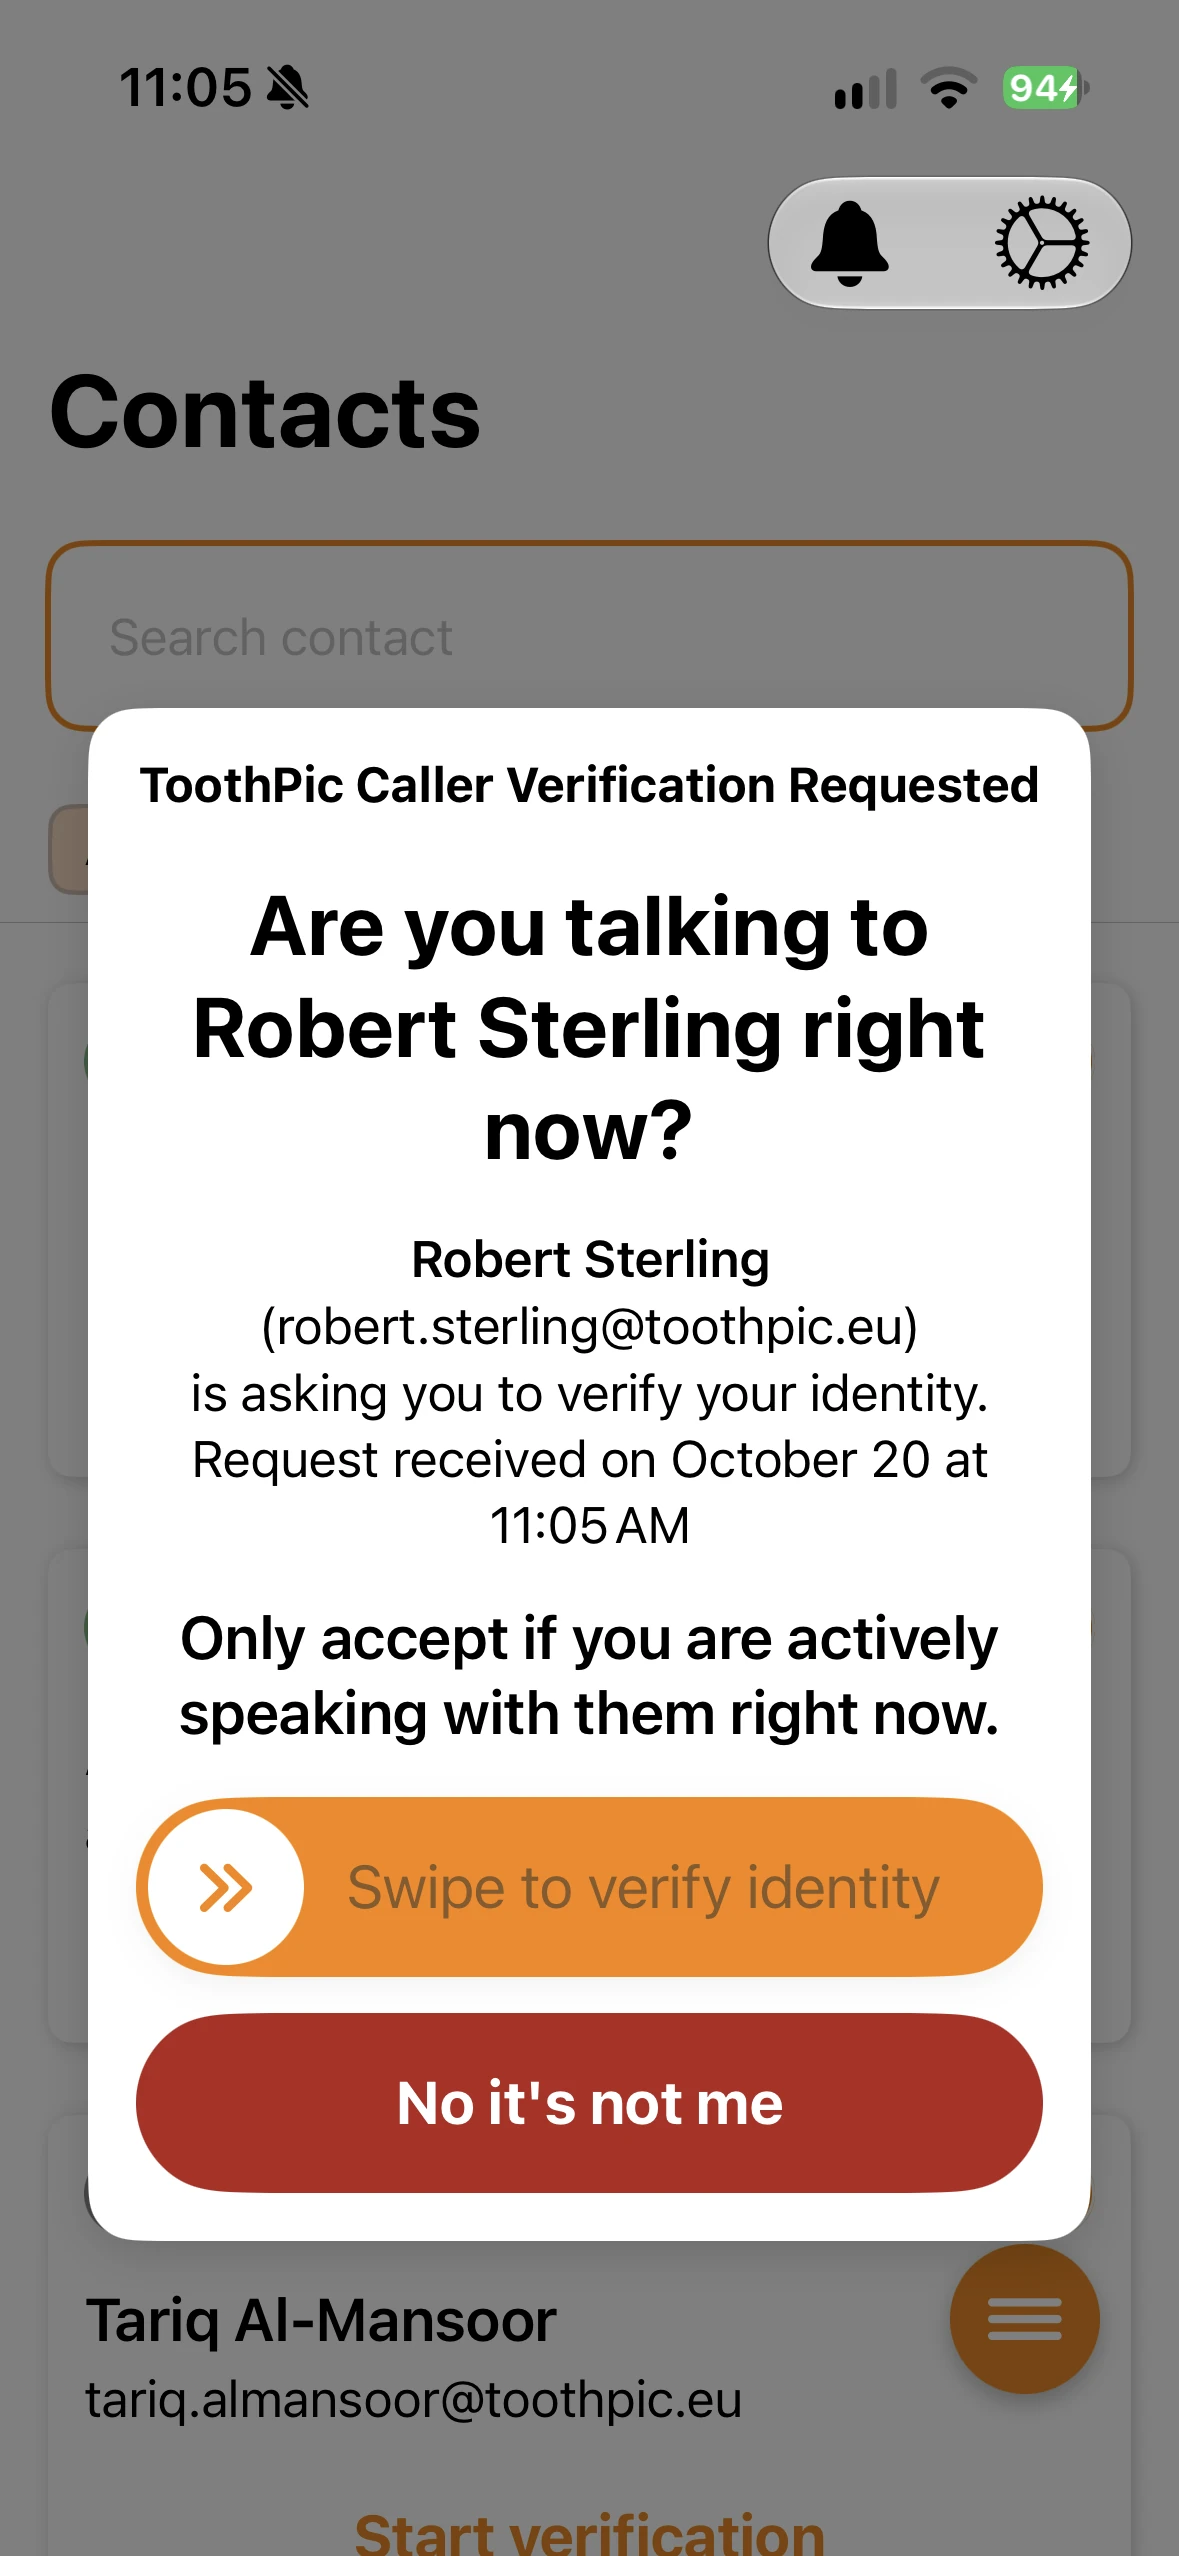
Confirm request
Camila gets an alert on his own iPhone and swipes to confirm.
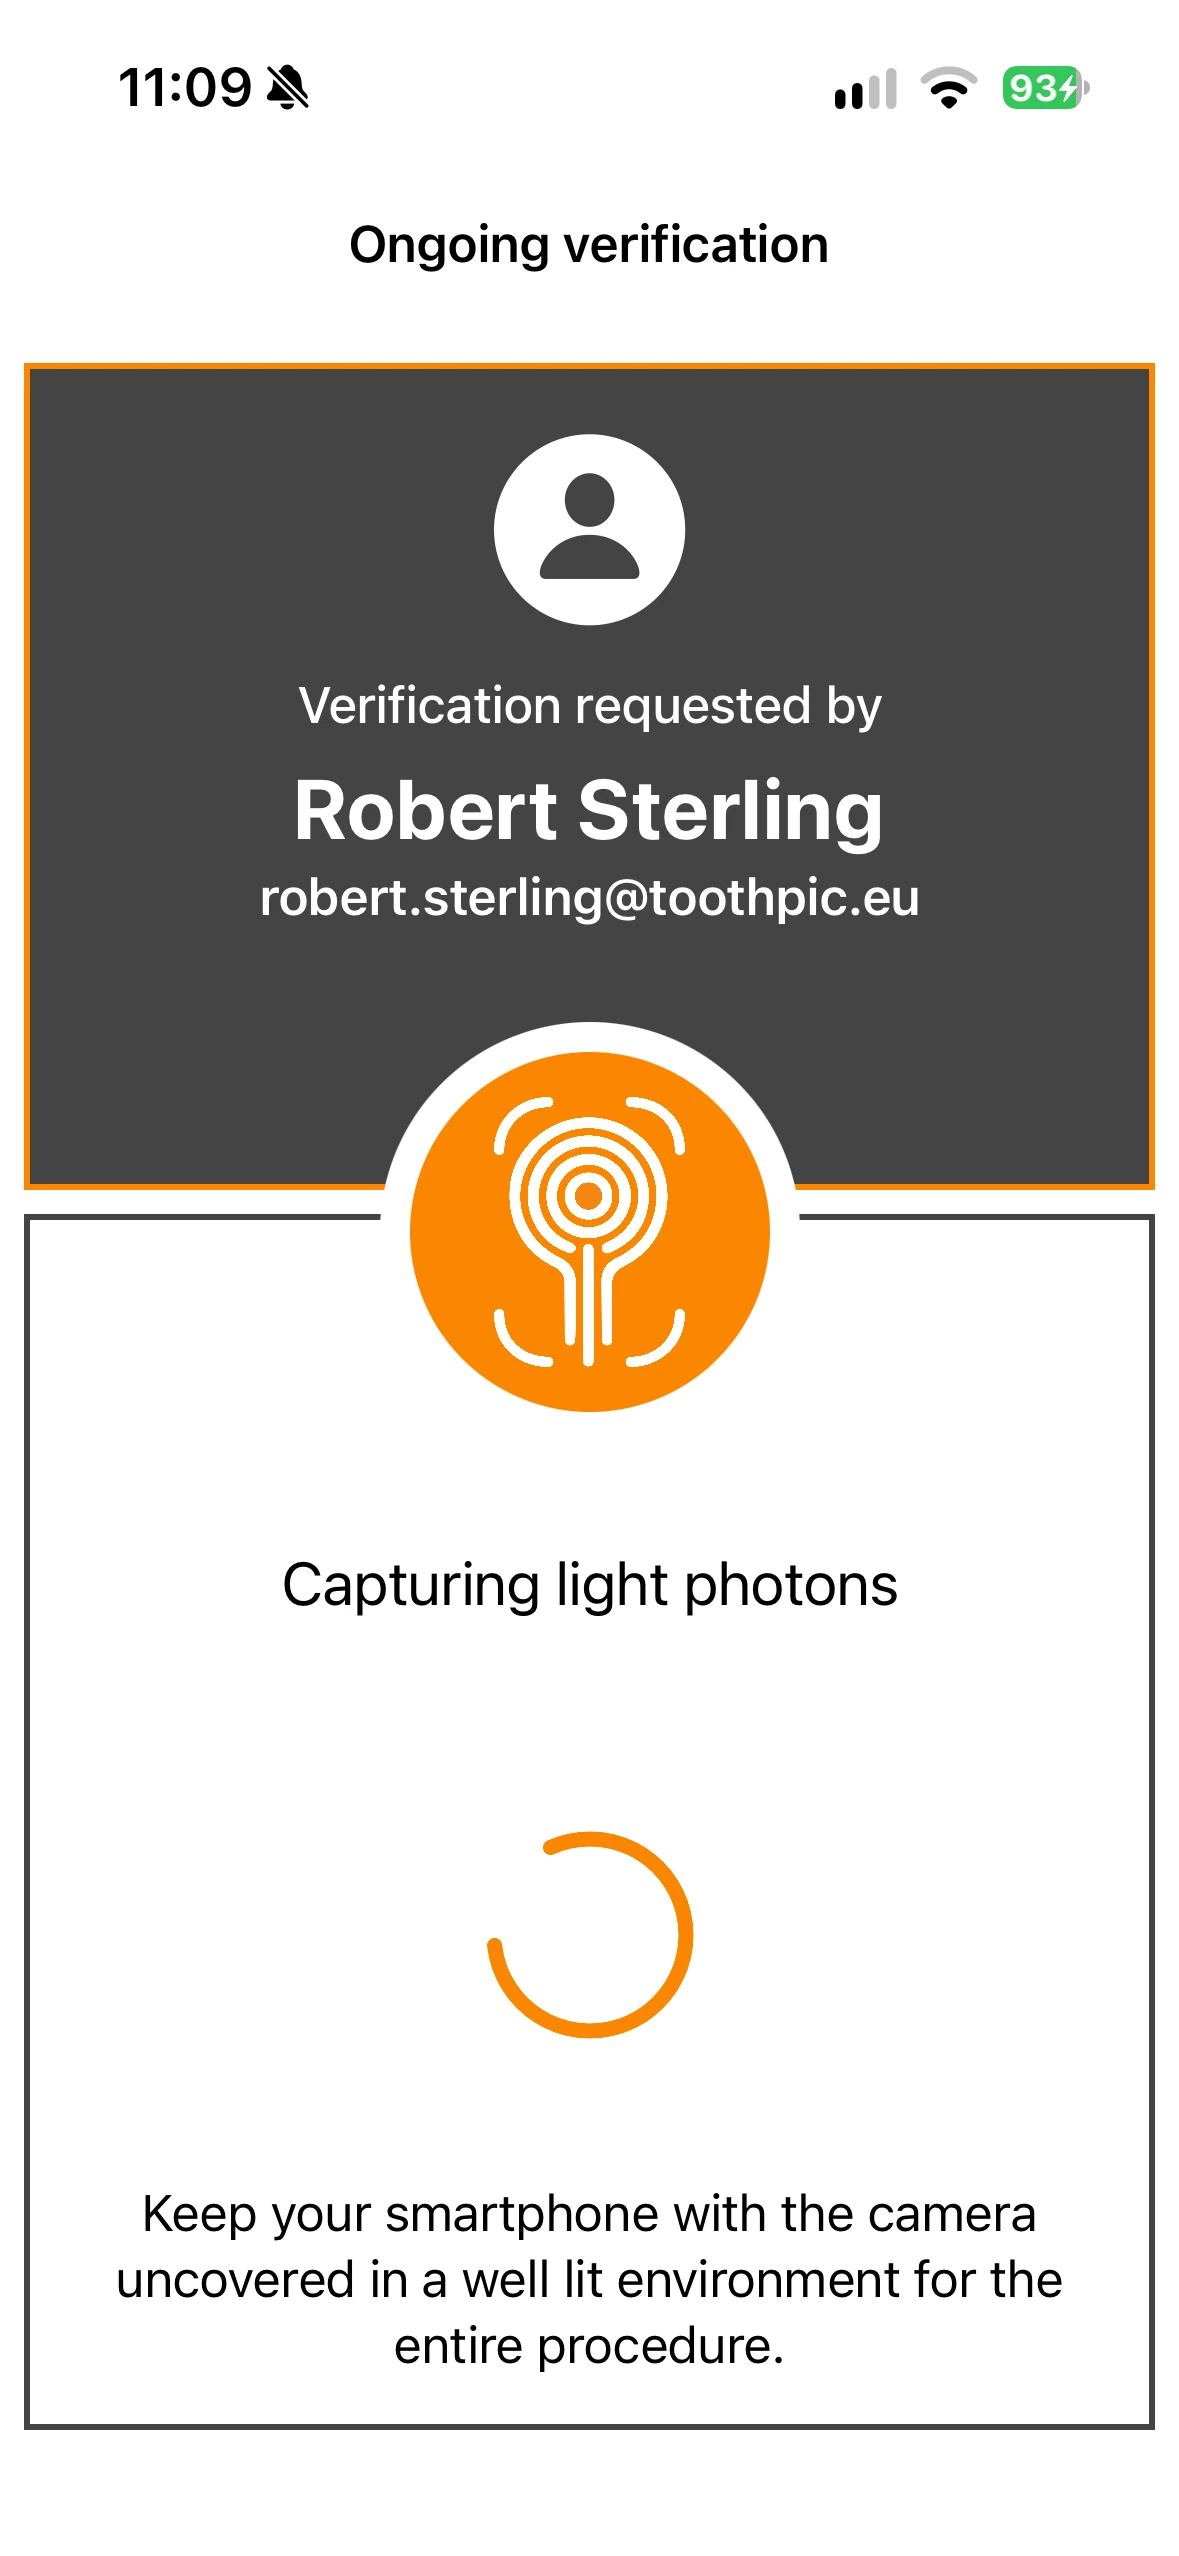
Photon capture
The SDK estimates the sensor fingerprint, rebuilds the key without exposing it in RAM, signs and purges it.
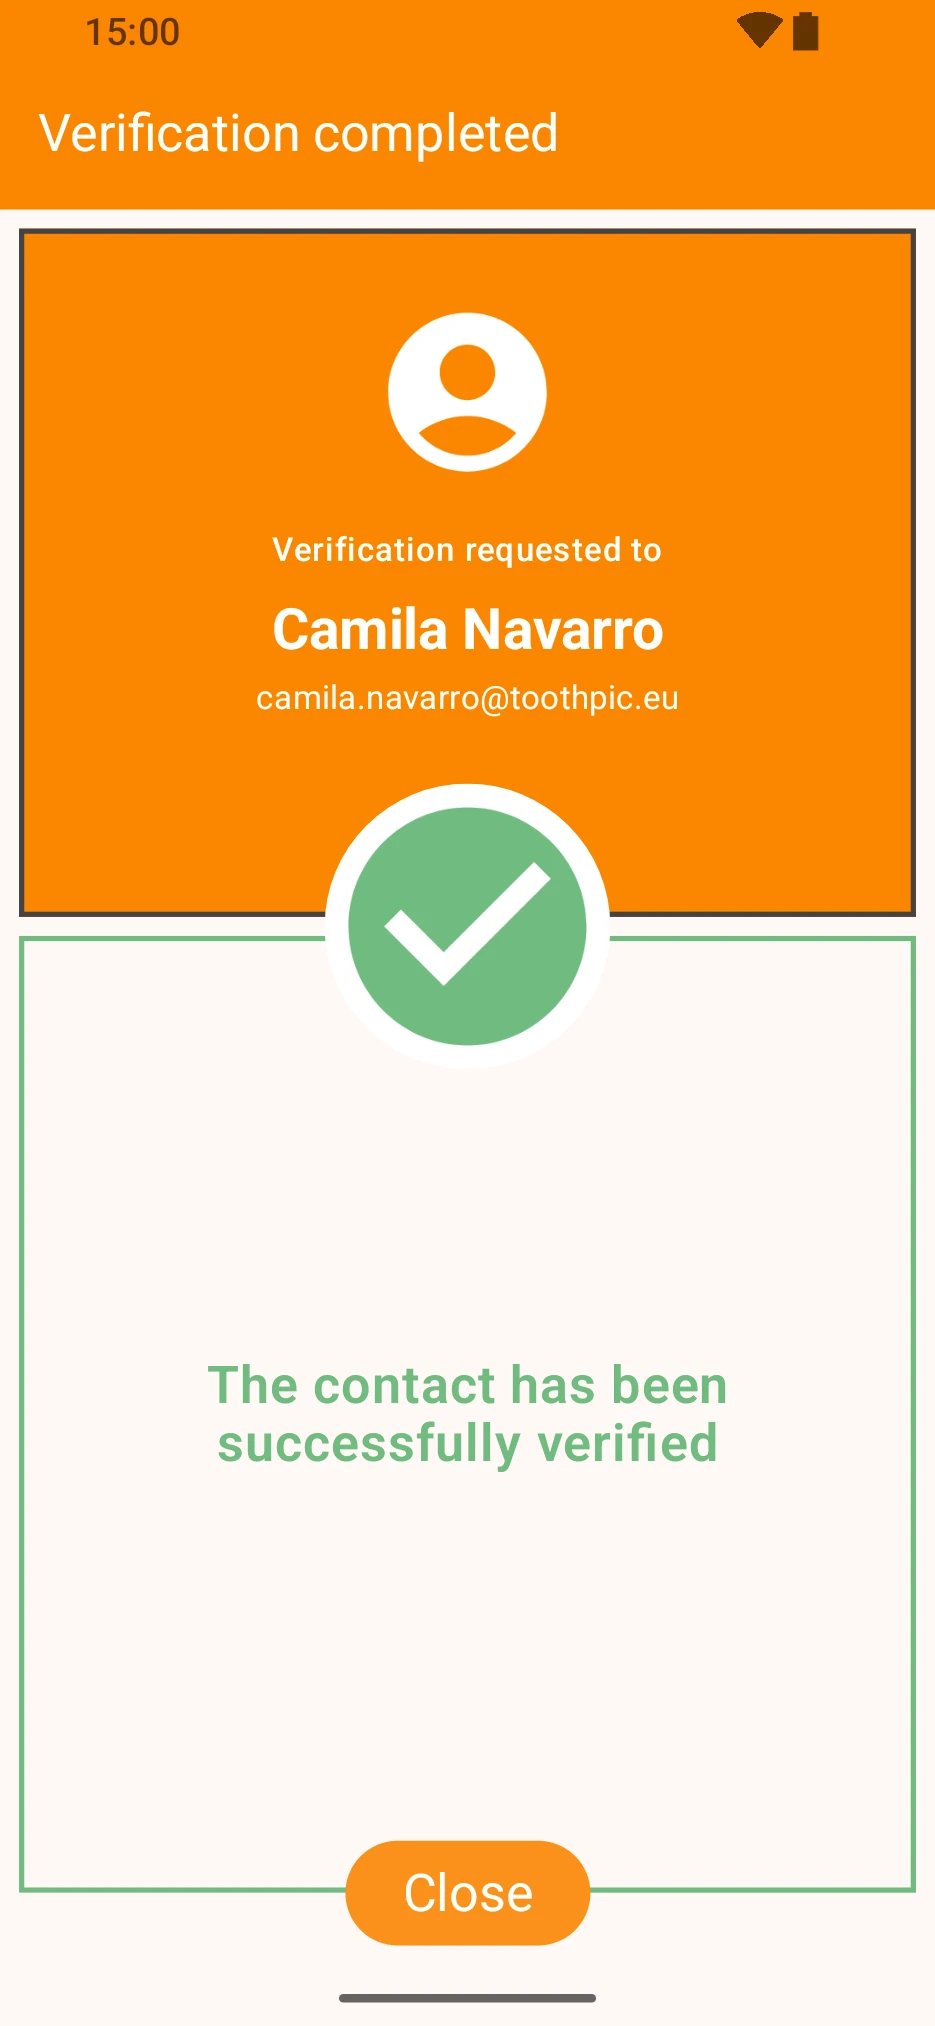
Verified ✓
Robert’s app checks the signature against Camila’s public key.
Where it’s used
Built for the moments that move money and trust.
Executive impersonation protection
Stops voice clones and video deepfakes of executives during live transactions and approvals. Also secures remote hiring against synthetic candidates.
Secure out-of-band channel
An alternative communication channel, giving tamper-proof proof of who was on the call.
IAM outage business continuity
Keys are bound to hardware sensors, not databases — verification keeps working when core IAM systems are offline.
Emergency backup for compromised IT
A clean verification path even if corporate IT, network or directories are fully compromised.
Why software-only security fails
AI attacks the top of the stack. We anchor at the bottom.
Generative models now defeat biometrics, software tokens and OTPs, and injection attacks bypass the camera feed entirely. Keys kept in the OS or firmware can still be stolen by system-level malware.
The ephemeral ideal. ToothPic never stores a credential. The key is rebuilt from the sensor only when needed and destroyed straight after — steal the storage and you still have nothing without the physical sensor.
Gartner recommendation
“Anchor digital identities to verifiable physical hardware sensors to neutralize synthetic deepfake injection attacks.”
Gartner, Emerging Tech: Startups to Watch for Deepfake Detection, April 2026. That is precisely what ToothPic does — and it answers two different briefs inside the same organisation.
For the CIO & CISO · Internal threats
Protect your people from social engineering
Employees are probed and targeted with deepfakes. ToothPic adds a decentralised, out-of-band channel bound to each phone’s sensor, so software credentials alone can never pass as a colleague.
For the CCO & CMO · External brand trust
Stop fake executives reaching your clients
Attackers impersonate executives on calls to push fraudulent transactions. Caller 1 instantly verifies Caller 2 is genuine, neutralising impersonation before money moves.
Make every high-value call provably genuine.
See a live caller verification end to end, then pilot it with an executive or treasury team.